
Preparing for a quantum-safe future takes collaboration across the entire technology ecosystem.
From silicon and firmware to protocols, certification, and system integration, the transition to Post-Quantum Cryptography (PQC) requires coordinated efforts across industries and technology partners.
In our latest case study, Infineon, an active member of the Charter of Trust PQC Working Group, shares practical insights from its PQC journey, including early preparation, crypto-agility, secure update mechanisms, and building long-term cyber resilience.
Explore the full case study to learn how Infineon is putting PQC into practice.
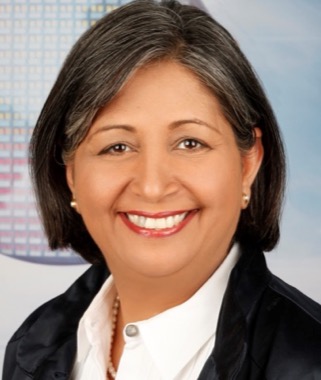
Preeti Ohri Khemani
Senior Director, Standards & Regulations, Edge Systems Division, Infineon
Senior Director, Standards & Regulations, Edge Systems Division, Infineon
“Infineon has successfully demonstrated a fully hybrid PQC implementation for the German national eID card. Hybrid implementations and crypto agility for post quantum cyber resilience are an important aspect for most implementers: security targets in the post quantum AI era will be shifting frequently.”
Download

PREVIOUS POST
Principle Use Cases – AES
NEXT POST
AI Policy Paper

You may also like
 Artificial Intelligence
AI Policy Paper
Artificial intelligence has become a critical component of modern industrial processes, cybersecurity operations, and digital infrastructure. As companies increasingly build and integrate their own AI capabilities, the need for secure, trustworthy, and compliant digital environments has never been more pressing.
In this paper, our AI Working Group provides a clear framework for organisations to navigate this landscape, marked by concentrated provider ecosystems, fragmented global regulations, and geopolitical supply chain risks, alongside the internal requirements necessary to build AI responsibly.
A key aspect is helping organisations prepare for the EU AI Act, based on the overarching principle that compliance cannot be treated as a simple checklist exercise, and should instead drive strategic transformation. Organisations are encouraged to ensure visibility over all AI systems in use, promoting alignment across technical, legal, and business functions. Strengthening governance is equally critical. Executive level oversight, supported by operational teams, should lead to consistent, iterative risk assessment throughout the AI lifecycle, ensuring that performance, ethical, legal, and operational risks are identified and addressed early.
Companies must also balance compliance investments against the financial and reputational risks of non compliance. The penalties under the AI Act are substantial. However, proactive preparation not only reduces exposure, it can also create a competitive advantage by enabling faster innovation, strengthening customer relationships and regulator trust, and reducing uncertainty in product development.
Looking ahead, organisations should treat AI governance as a long term, adaptive discipline. Regulation and technology will continue evolving, and resilience depends on flexible policies, modular system architectures, and scalable governance processes.
Continuous monitoring of regulatory developments, active participation in standards setting activities, and sustained investment in skills are essential to fostering a responsible AI culture centred around a holistic understanding of compliance.
Please download the full report below.
In this paper, our AI Working Group provides a clear framework for organisations to navigate this landscape, marked by concentrated provider ecosystems, fragmented global regulations, and geopolitical supply chain risks, alongside the internal requirements necessary to build AI responsibly.
A key aspect is helping organisations prepare for the EU AI Act, based on the overarching principle that compliance cannot be treated as a simple checklist exercise, and should instead drive strategic transformation. Organisations are encouraged to ensure visibility over all AI systems in use, promoting alignment across technical, legal, and business functions. Strengthening governance is equally critical. Executive level oversight, supported by operational teams, should lead to consistent, iterative risk assessment throughout the AI lifecycle, ensuring that performance, ethical, legal, and operational risks are identified and addressed early.
Companies must also balance compliance investments against the financial and reputational risks of non compliance. The penalties under the AI Act are substantial. However, proactive preparation not only reduces exposure, it can also create a competitive advantage by enabling faster innovation, strengthening customer relationships and regulator trust, and reducing uncertainty in product development.
Looking ahead, organisations should treat AI governance as a long term, adaptive discipline. Regulation and technology will continue evolving, and resilience depends on flexible policies, modular system architectures, and scalable governance processes.
Continuous monitoring of regulatory developments, active participation in standards setting activities, and sustained investment in skills are essential to fostering a responsible AI culture centred around a holistic understanding of compliance.
Please download the full report below.
Read more
February 11, 2026
•
 External Engagement
Report about Hybrid Threats presented at MSC 2025
Navigating Cybersecurity in an Era of Hybrid Threats
As hybrid threats continue to evolve, cybersecurity has never been more critical. The latest Charter of Trust report, launched at the Munich Security Conference, presents exclusive insights from leading CISOs and CSOs across our Partner network. This report provides a comprehensive analysis of the shifting threat landscape and the strategic actions necessary to enhance global resilience.
Key Insights from the Report
- The Growing Threat Landscape: Cyber adversaries are emerging across the globe, leveraging increasingly sophisticated tactics. Advanced threat detection and multi-layered defense strategies are no longer optional but essential.
- Breaking Down Security Silos: Cyber threats are constantly evolving—organizations cannot afford to wait. A proactive, collaborative approach is critical, fostering open dialogue across industries and sectors.
- Leadership in Collective Defense: Multinational corporations have a unique responsibility to lead in both technical defense and talent development, while also advancing zero trust architectures to mitigate risks effectively.
Collaboration as the Foundation of Cyber Resilience
The experiences of Charter of Trust partners highlight the importance of collective action in addressing the complexities of hybrid threats. Operating in high-stakes environments, these organizations provide valuable lessons for improving industry-wide preparedness.
A Call for Unified Action
Hybrid threats do not recognize national or industry boundaries—our response must be equally interconnected. As both prime targets and key defenders, multinational corporations are uniquely positioned to drive unified, strategic action. Initiatives like the Charter of Trust serve as a model for global collaboration, strengthening the cybersecurity ecosystem and paving the way for a more secure future.
We extend our gratitude to the CISOs and CSOs who contributed their expertise to this publication, including: Kyle Oetken (AES), Haydn Griffiths (Allianz), Paul Bayle (Atos), Christoph Peylo (Bosch), Morten Pors Simonsen (Danfoss), Koos Lodewijkx (IBM), Raphael Otto (Infineon), Natalia Oropeza (Siemens), Norbert Vetter (TÜV SÜD)
As hybrid threats continue to evolve, cybersecurity has never been more critical. The latest Charter of Trust report, launched at the Munich Security Conference, presents exclusive insights from leading CISOs and CSOs across our Partner network. This report provides a comprehensive analysis of the shifting threat landscape and the strategic actions necessary to enhance global resilience.
Key Insights from the Report
- The Growing Threat Landscape: Cyber adversaries are emerging across the globe, leveraging increasingly sophisticated tactics. Advanced threat detection and multi-layered defense strategies are no longer optional but essential.
- Breaking Down Security Silos: Cyber threats are constantly evolving—organizations cannot afford to wait. A proactive, collaborative approach is critical, fostering open dialogue across industries and sectors.
- Leadership in Collective Defense: Multinational corporations have a unique responsibility to lead in both technical defense and talent development, while also advancing zero trust architectures to mitigate risks effectively.
Collaboration as the Foundation of Cyber Resilience
The experiences of Charter of Trust partners highlight the importance of collective action in addressing the complexities of hybrid threats. Operating in high-stakes environments, these organizations provide valuable lessons for improving industry-wide preparedness.
A Call for Unified Action
Hybrid threats do not recognize national or industry boundaries—our response must be equally interconnected. As both prime targets and key defenders, multinational corporations are uniquely positioned to drive unified, strategic action. Initiatives like the Charter of Trust serve as a model for global collaboration, strengthening the cybersecurity ecosystem and paving the way for a more secure future.
We extend our gratitude to the CISOs and CSOs who contributed their expertise to this publication, including: Kyle Oetken (AES), Haydn Griffiths (Allianz), Paul Bayle (Atos), Christoph Peylo (Bosch), Morten Pors Simonsen (Danfoss), Koos Lodewijkx (IBM), Raphael Otto (Infineon), Natalia Oropeza (Siemens), Norbert Vetter (TÜV SÜD)
Read more
February 14, 2025
•
 Security by Default
 in view of major Cybersecurity Regulations
Navigate the Cybersecurity Regulation Maze with Ease
The Charter of Trust is here to simplify the complexity and guide you through the ever-evolving regulatory landscape.
In today's digitized world, cybersecurity plays a pivotal role in maintaining global stability, economic resilience, and individual privacy. Various regulations have been implemented to safeguard individuals, businesses, and infrastructure from ever-evolving cyber threats. Each regulation, while differing in scope and focus by region, aims to protect against breaches, data leaks, and other malicious activities that could disrupt operations and compromise sensitive information.
At the heart of the Charter of Trust lies a commitment to sharing best practices. Our Security by Default Working Group has meticulously analyzed vast amounts of regulatory texts to provide a clear and concise overview of security by default adoption across key global regions.
Stay Ahead of Cyber Risks with Expert Insights
Our latest report is a vital resource for organizations aiming to effectively manage cybersecurity risks and protect their assets. Covering major regulations from the European Union, India, Japan, People's Republic of China, Singapore, the United Kingdom, and the United States, this report offers valuable insights into compliance requirements worldwide.
The principle of Security by Default, as advocated by the Charter of Trust, provides a universal standard for organizations to meet compliance requirements effectively. By embedding security measures from the outset, organizations can ensure compliance with regulations, foster trust with customers, safeguard their operations, and strengthen their market position. This approach not only helps organizations meet their legal obligations but also enhances their reputation and competitive advantage.
Strengthen Compliance, Build Trust, and Gain a Competitive Edge
By embedding security measures from the outset, businesses can:
- Ensure compliance with international regulations
- Build and maintain trust with customers and stakeholders
- Safeguard operations from cybersecurity threats
- Strengthen their market position with a proactive security approach
The publication shows that regulators worldwide have taken different approaches to pursuing common cybersecurity goals, leading to varied and sometimes conflicting regulatory frameworks. This complexity can make it challenging for organizations to navigate the cybersecurity landscape and ensure compliance with all relevant regulations.
This document serves as a roadmap to better navigate this complex landscape, thereby highlighting the benefits of aligning current cybersecurity regulations worldwide. It supports the Charter of Trust's mission to create a secure digital environment for innovation. By following the guidelines outlined in this document, organizations can effectively manage their cybersecurity risks, protect their assets, and contribute to a more secure digital world.
Don't get lost in the regulatory jungle — get the clarity you need today and download the full report below
The Charter of Trust is here to simplify the complexity and guide you through the ever-evolving regulatory landscape.
In today's digitized world, cybersecurity plays a pivotal role in maintaining global stability, economic resilience, and individual privacy. Various regulations have been implemented to safeguard individuals, businesses, and infrastructure from ever-evolving cyber threats. Each regulation, while differing in scope and focus by region, aims to protect against breaches, data leaks, and other malicious activities that could disrupt operations and compromise sensitive information.
At the heart of the Charter of Trust lies a commitment to sharing best practices. Our Security by Default Working Group has meticulously analyzed vast amounts of regulatory texts to provide a clear and concise overview of security by default adoption across key global regions.
Stay Ahead of Cyber Risks with Expert Insights
Our latest report is a vital resource for organizations aiming to effectively manage cybersecurity risks and protect their assets. Covering major regulations from the European Union, India, Japan, People's Republic of China, Singapore, the United Kingdom, and the United States, this report offers valuable insights into compliance requirements worldwide.
The principle of Security by Default, as advocated by the Charter of Trust, provides a universal standard for organizations to meet compliance requirements effectively. By embedding security measures from the outset, organizations can ensure compliance with regulations, foster trust with customers, safeguard their operations, and strengthen their market position. This approach not only helps organizations meet their legal obligations but also enhances their reputation and competitive advantage.
Strengthen Compliance, Build Trust, and Gain a Competitive Edge
By embedding security measures from the outset, businesses can:
- Ensure compliance with international regulations
- Build and maintain trust with customers and stakeholders
- Safeguard operations from cybersecurity threats
- Strengthen their market position with a proactive security approach
The publication shows that regulators worldwide have taken different approaches to pursuing common cybersecurity goals, leading to varied and sometimes conflicting regulatory frameworks. This complexity can make it challenging for organizations to navigate the cybersecurity landscape and ensure compliance with all relevant regulations.
This document serves as a roadmap to better navigate this complex landscape, thereby highlighting the benefits of aligning current cybersecurity regulations worldwide. It supports the Charter of Trust's mission to create a secure digital environment for innovation. By following the guidelines outlined in this document, organizations can effectively manage their cybersecurity risks, protect their assets, and contribute to a more secure digital world.
Don't get lost in the regulatory jungle — get the clarity you need today and download the full report below
Read more
February 13, 2025
•