
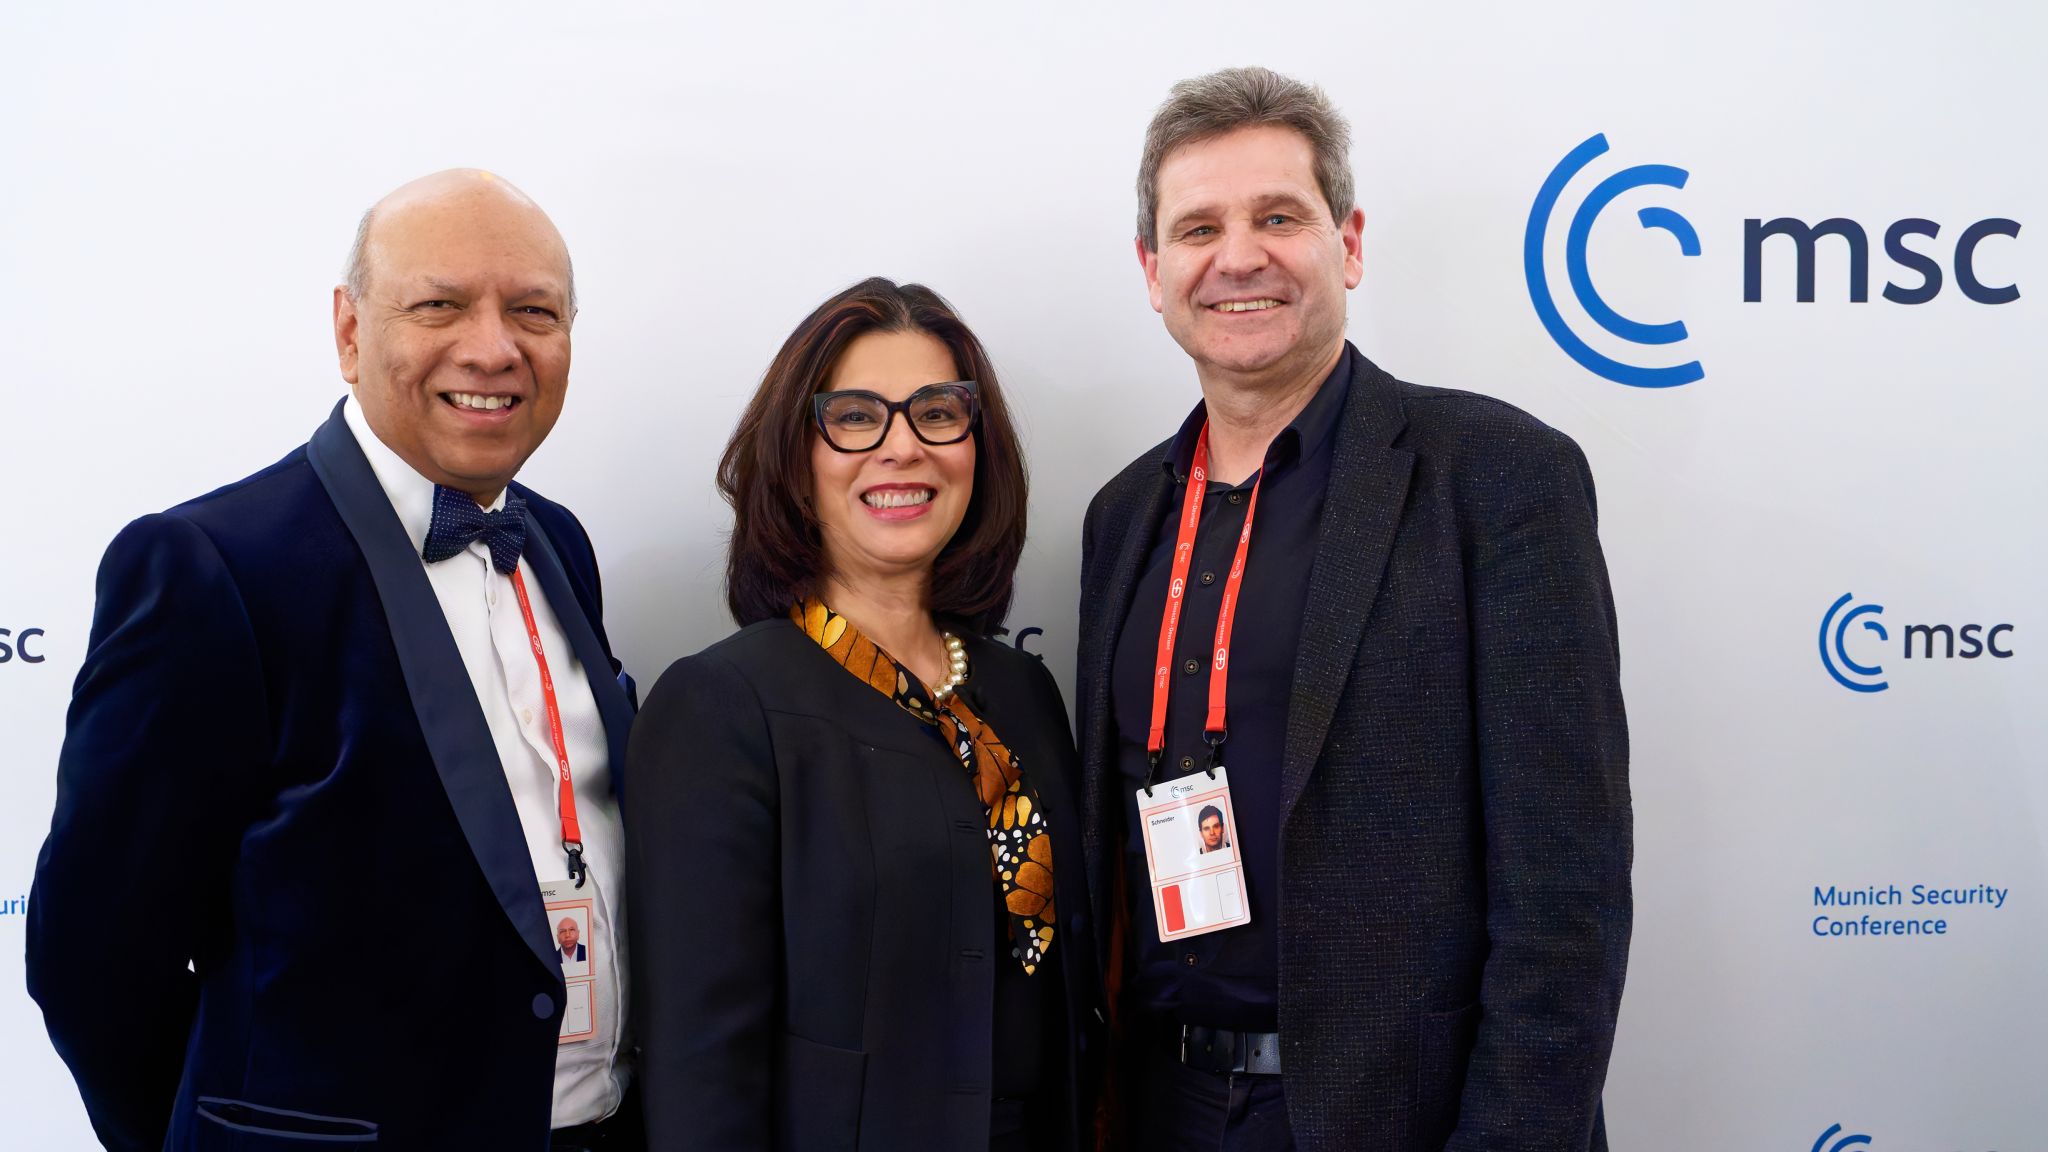
We are honoured to announce that Dr. Ralf Schneider, Senior Fellow and Head of Cybersecurity and NextGenIT Think Tank at Allianz and Dr. Sumit Chanda, Chief Operating Officer at Atos Group Security have been elected as new co-chairs of the Charter of Trust during our last Board of Directors meeting in Munich.
The Partners and Associated Partners thanked Natalia Oropeza, Global Chief Cybersecurity Officer at Siemens, for her engagement and steady leadership during her term as Chairwoman. In her tenure, the Charter of Trust underwent important internal and external changes. What first stands out is the smooth integration of the four working groups, which made the Charter of Trust more agile, leaner and more efficient. It is also safe to say that the alliance has never had such a high level of exposure externally, due to the Charter of Trust partners continuous dedication to the mission of the alliance.
In the spirit of industry collaboration, Natalia Oropeza expressed her support to our new Co-Chairs and said how “incredibly proud of what we have achieved together, welcoming new partners, strengthening our structure, and elevating the Charter of Trust's impact on the global cybersecurity landscape. Collaboration has been at the heart of our success, and I am confident that Dr. Sumit Chanda and Dr. Ralf Schneider as Co-Chairs, the Charter will continue to drive meaningful progress towards a more secure digital world."
For the first time in its history, the Charter of Trust will be co-chaired. Dr. Ralf Schneider from Allianz and Dr. Sumit Chanda from Atos who have decades of experience in the world of cybersecurity and have been active within the alliance for several years now. Both unite an intrinsic motivation to foster inter- and intra-sector collaboration as well as the continuous sharing of knowledge between the Partners and Associated Partners of the Charter of Trust.
For the next year the co-chairs aim to amplify the number of Partners and Associated Partners. This growth, however, should still preserve the unique features of the Charter of Trust as a large practitioner organization with member from all over the world. Expanding into new sectors and new countries is a key target for the new leadership team, so that the Alliance can continue to engage with stakeholders at the highest level.
Dr. Sumit Chanda underlined that “The Charter of Trust’s role is to promote a safe and trusted digital work. Its unique partnership blend of large organisations, working across 190 countries, and across several sectors, has enabled it to make significant progress under the leadership of Mrs. Natalia Oropeza. I would like to thank her for these great achievements. Along with Dr. Ralf Schneider from Allianz, we welcome the opportunity to build on her work as the Co-Chairs of Charter of Trust.”
Ralf Schneider added that “In dynamic times with more risks, more uncertainty, and more unknowns, we as the Charter of Trust step up – to provide stability, promote reliability, and foster trust. This is our mission today and tomorrow.”.
Download

PREVIOUS POST
Richards Skalt takes over the Advocacy Workstream
NEXT POST
Charter of Trust launches Cyber Deterrence in the private sector

You may also like
 Cyber Deterrence
Charter of Trust launches Cyber Deterrence in the private sector
The Charter of Trust has launched its Cyber Deterrence Working Group to address a central gap in today’s cybersecurity landscape: the disconnect between strong defensive investments and the persistent economic attractiveness of cybercrime. The group brings together industry partners to develop and validate practical deterrence methods that raise attacker cost and risk across sectors and borders.
Read more
June 30, 2026
•
Post-Quantum Cryptography
Decrypting the Future: Global Timelines for PostQuantum Cryptography and why they matter
The transition to post-quantum cryptography is not a future problem — it is a present one. The threat of adversaries harvesting encrypted data today for decryption once quantum computing matures means that organizations with long-lived data and systems are already exposed. Waiting for cryptographically relevant quantum computers to arrive before acting is not a viable risk management strategy.
Exposure is not uniform across sectors. Financial services, government and defense, operational technology, and healthcare face the sharpest quantum risk, driven by decades-long data retention obligations, slow system replacement cycles, and the societal consequences of cryptographic failure. For these sectors, PQC readiness has moved from best practice to strategic imperative.
Globally, the direction of travel is clear. The United States, European Union, United Kingdom, Singapore, and Australia have each established structured PQC transition frameworks, with mandatory deadlines converging around the late 2020s and 2030. Organizations operating across jurisdictions should expect compounding compliance requirements and align migration plans accordingly.
At the same time, the geopolitical dimension of PQC standardization is becoming increasingly salient. The emergence of a “splinternet” infrastructure, characterized by regionally fragmented digital ecosystems, suggests that cryptographic standards diverge along political and strategic lines. As a result, organizations must not only manage technical migration but also navigate a politically charged landscape in which interoperability, regulatory alignment, and long-term cryptographic agility become critical strategic considerations.
This paper offers a comparative overview of regional PQC transition frameworks and identifies the business and systemic risks associated with quantum-vulnerable cryptography, providing insights for organizations preparing for the transition to post-quantum cryptography. Overall, PQC migration is a strategic transformation, not a technical patch. Cryptographic inventory, governance structures, crypto-agility, and supply chain engagement are as central to success as algorithm selection — and organizations that treat PQC readiness as an architectural and organizational challenge will be best positioned as quantum risks continue to mature.
Exposure is not uniform across sectors. Financial services, government and defense, operational technology, and healthcare face the sharpest quantum risk, driven by decades-long data retention obligations, slow system replacement cycles, and the societal consequences of cryptographic failure. For these sectors, PQC readiness has moved from best practice to strategic imperative.
Globally, the direction of travel is clear. The United States, European Union, United Kingdom, Singapore, and Australia have each established structured PQC transition frameworks, with mandatory deadlines converging around the late 2020s and 2030. Organizations operating across jurisdictions should expect compounding compliance requirements and align migration plans accordingly.
At the same time, the geopolitical dimension of PQC standardization is becoming increasingly salient. The emergence of a “splinternet” infrastructure, characterized by regionally fragmented digital ecosystems, suggests that cryptographic standards diverge along political and strategic lines. As a result, organizations must not only manage technical migration but also navigate a politically charged landscape in which interoperability, regulatory alignment, and long-term cryptographic agility become critical strategic considerations.
This paper offers a comparative overview of regional PQC transition frameworks and identifies the business and systemic risks associated with quantum-vulnerable cryptography, providing insights for organizations preparing for the transition to post-quantum cryptography. Overall, PQC migration is a strategic transformation, not a technical patch. Cryptographic inventory, governance structures, crypto-agility, and supply chain engagement are as central to success as algorithm selection — and organizations that treat PQC readiness as an architectural and organizational challenge will be best positioned as quantum risks continue to mature.
Read more
April 07, 2026
•
Post-Quantum Cryptography
A Quantum Leap for Cybersecurity: The Charter of Trust’s PQC Ambition
The Charter of Trust is taking decisive steps to secure our digital future in the quantum era. As quantum computing advances, the risks to today’s cryptographic systems grow ever more urgent. Our dedicated working group is leading the way in raising awareness, promoting standards-based migration, and fostering collaboration across industries, governments, and academia. Together, we are committed to a proactive, well-coordinated, and risk-driven transition to post-quantum cryptography—ensuring digital trust and resilience for generations to come. Discover our vision and join us as we shape a secure digital world for the quantum age.
Read more
November 18, 2026
•