
 PUBLICATIONS
 EVENTS
 NEWS
 Post-Quantum Cryptography
Decrypting the Future: Global Timelines for PostQuantum Cryptography and why they matter
The transition to post-quantum cryptography is not a future problem — it is a present one. The threat of adversaries harvesting encrypted data today for decryption once quantum computing matures means that organizations with long-lived data and systems are already exposed. Waiting for cryptographically relevant quantum computers to arrive before acting is not a viable risk management strategy.
Exposure is not uniform across sectors. Financial services, government and defense, operational technology, and healthcare face the sharpest quantum risk, driven by decades-long data retention obligations, slow system replacement cycles, and the societal consequences of cryptographic failure. For these sectors, PQC readiness has moved from best practice to strategic imperative.
Globally, the direction of travel is clear. The United States, European Union, United Kingdom, Singapore, and Australia have each established structured PQC transition frameworks, with mandatory deadlines converging around the late 2020s and 2030. Organizations operating across jurisdictions should expect compounding compliance requirements and align migration plans accordingly.
At the same time, the geopolitical dimension of PQC standardization is becoming increasingly salient. The emergence of a “splinternet” infrastructure, characterized by regionally fragmented digital ecosystems, suggests that cryptographic standards diverge along political and strategic lines. As a result, organizations must not only manage technical migration but also navigate a politically charged landscape in which interoperability, regulatory alignment, and long-term cryptographic agility become critical strategic considerations.
This paper offers a comparative overview of regional PQC transition frameworks and identifies the business and systemic risks associated with quantum-vulnerable cryptography, providing insights for organizations preparing for the transition to post-quantum cryptography. Overall, PQC migration is a strategic transformation, not a technical patch. Cryptographic inventory, governance structures, crypto-agility, and supply chain engagement are as central to success as algorithm selection — and organizations that treat PQC readiness as an architectural and organizational challenge will be best positioned as quantum risks continue to mature.
Read more
April 07, 2026
• 5 min read
Post-Quantum Cryptography
A Quantum Leap for Cybersecurity: The Charter of Trust’s PQC Ambition
The Charter of Trust is taking decisive steps to secure our digital future in the quantum era. As quantum computing advances, the risks to today’s cryptographic systems grow ever more urgent. Our dedicated working group is leading the way in raising awareness, promoting standards-based migration, and fostering collaboration across industries, governments, and academia. Together, we are committed to a proactive, well-coordinated, and risk-driven transition to post-quantum cryptography—ensuring digital trust and resilience for generations to come. Discover our vision and join us as we shape a secure digital world for the quantum age.
Read more
October 23, 2026
• 5 min read
 Artificial Intelligence
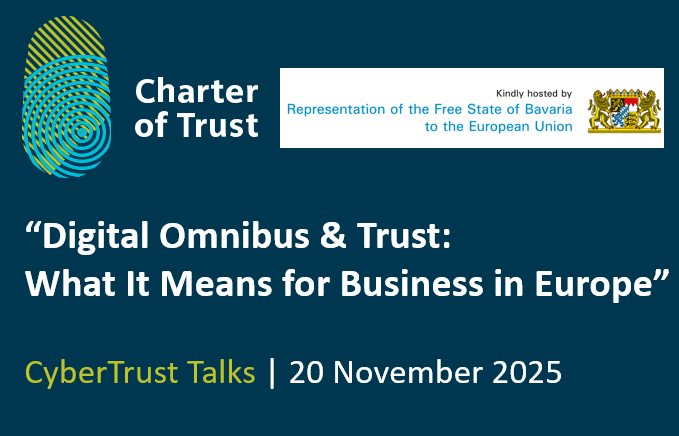
3rd CyberTrust Talk - Digital Omnibus & Trust - What it Means for Business in Europe?
Join us for a timely and dynamic edition focused on “Digital Omnibus & Trust: What It Means for Business in Europe” kindly hosted by the Representation of the Free State of Bavaria to the EU on November 20, 2025 at 11:00 AM (Central European Time) for a lunch event filled with insightful discussions on cybersecurity and trust in the digital age.
With the European Commission unveiling its landmark Digital Omnibus Package just one day before, this event is your exclusive opportunity to be among the first to explore its real-world impact on business and the digital economy across Europe.
What to Expect:
Opening remarks by:
Dr. Armin Hartmuth, Director, Representation of the Free State of Bavaria to the European Union
Dr. Sumit Chanda, COO, Atos Group Security & Business Lines CISO, and Co-Chair of the Charter of Trust.
Keynote Address:
Despina Spanou, Deputy Director General for Cybersecurity and Trust, European Commission (DG CNECT), will share first-hand insights into the objectives and expected impact of the Digital Omnibus Package.
Expert Panel Discussion featuring:Moderated by Sudhir Ethiraj, Global Head of Cybersecurity Office, CEO Business Unit Cybersecurity Services, TÜV SÜD.
Despina Spanou, Deputy Director General for Cybersecurity and Trust, European Commission (DG CNECT)
Kia Slæbæk Jensen, Cyber Advisor, Permanent Representation of Denmark to the EU
Suzanne Button, Field CTO EMEA, Elastic
Tomas Jakimavicius, Director European Government Affairs, Microsoft
Yana Humen, AI and Cybersecurity Policy Manager, Government and Regulatory Affairs, IBM
Interactive Q&A: Bring your questions and join the conversation on regulatory coherence, innovation, and the future of digital governance in Europe.
Closing remarks by Maria del Pino Gonzalez-Junco, Director of the Charter of Trust
Networking Lunch: Connect with peers, policymakers, and industry leaders in an informal setting.
Why attend?
Gain first-hand insights into the EU’s Digital Omnibus Package—straight from the policymakers and experts shaping it.
Understand the immediate implications for your business and how to navigate upcoming changes.
Be part of a strategic dialogue that could influence the future of digital regulation in Europe.
Read more
November 20, 2025
• 5 min read
 Artificial Intelligence
Read the Charter's contribution to the European Commission's public consultation on the Digital Omnibus Package
The rapid expansion of EU digital regulation has strengthened security, privacy, and trust, but it has also created overlapping obligations, inconsistent timelines, and administrative complexity. The Digital Omnibus Package provides a timely opportunity to streamline these rules, ensure greater coherence, and enable businesses to focus resources on resilience and innovation rather than redundant compliance tasks.
The Charter of Trust welcomes the Commission’s initiative to harmonize digital regulations across the EU, aiming to reduce administrative burdens while maintaining high standards of security and privacy. Representing the unified views of its Partners, this paper addresses all key legislation within the scope of the Digital Omnibus and offers comprehensive recommendations. It emphasizes the need for a unified incident reporting system, risk-based notification requirements, and fair compliance processes to minimize regulatory overlap. The Charter calls for clearer liability clauses, global recognition of certifications, and stronger supply chain security.
In data regulation, the Charter advocates ensuring alignment between the rules on data intermediation services under the DGA and B2B data sharing under the Data Act and extending exemptions to mid-cap companies, all while safeguarding trade secrets. For artificial intelligence, the paper recommends a phased approach to new requirements, integrated conformity assessments, harmonized compliance templates, and clear definitions, supported by sector-specific guidance and transparent AI categorization. The Charter also encourages the European Commission to ensure that ePrivacy reform is future-proof, fosters innovation, and reflects the needs of both businesses and consumers. Finally, it recommends robust security standards and cross-border recognition for the EU Business Wallet, with industry involvement in technical standards and integration with data access systems.
Collectively, these measures are designed to foster innovation, resilience, and trust in the EU’s digital landscape, allowing businesses to thrive in a coherent and future-ready regulatory environment.
Read more
October 14, 2025
• 5 min read
 Post-Quantum Cryptography
An Important Step Towards Security in a Post-Quantum World
By Julian Meyrick, IBM Managing Partner and Vice President, Security Strategy Risk & Compliance, Security Transformation Services and Lars Reger, NXP Executive Vice President and Chief Technology Officer
After six years of careful analysis, NIST has announced the first cryptographic algorithms that will allow us to maintain the highest levels of security in a post-quantum world – what we also refer to as ‘quantum-safe cryptography’. And while first quantum-safe products are already here – there is still much to be done. The selected algorithms won’t immediately lend themselves to existing resource-constrained platforms. Within organizations like the Charter of Trust, we can find the necessary experts working together to resolve these issues and support the industry with the pending cryptography transition, which should begin now – even though quantum computers of today are not yet able to break modern encryption.
After six years of careful analysis, NIST has announced the first cryptographic algorithms that will allow us to maintain the highest levels of security in a post-quantum world – what we also refer to as ‘quantum-safe cryptography’. And while first quantum-safe products are already here – there is still much to be done. The selected algorithms won’t immediately lend themselves to existing resource-constrained platforms. Within organizations like the Charter of Trust, we can find the necessary experts working together to resolve these issues and support the industry with the pending cryptography transition, which should begin now – even though quantum computers of today are not yet able to break modern encryption.
Read more
September 13, 2022
• 5 min read
 Post-Quantum Cryptography
Embedded Security in a Post-Quantum Computing World
Wolfgang Steinbauer, Head of Crypto & Security, NXP Semiconductors, explains how quantum computing has the potential to play a significant role in advancing our scientific knowledge and society in the coming decades, yet challenges the mechanisms we use today to secure information. This is why Charter of Trust Partners NXP, Infineon, and IBM are working on product solutions for a post-quantum future with long-term security.
Read more
January 14, 2022
• 5 min read